Cyber Security
Moving SSH from its default port can reduce routine connection attempts in logs. It does not make the service invisible, and it does not stop a target...
During a cyber incident, teams face pressure to restore service quickly. Actions taken in the first minutes can affect whether the attacker remains ac...
The OWASP Top 10 is an awareness document that groups important web application security risks. It can help a team start a review, but it is not a com...
Wi-Fi security depends on the router, the wireless encryption setting and the devices that join the network. A hidden network name or a changed SSID i...
Social engineering works by influencing a person to reveal information, approve access or move money. The message may arrive by email, phone, chat or ...
Data security work begins by understanding what personal data a system holds, why it is processed and which people or services can access it. GDPR and...
A strict Content Security Policy can block scripts, styles, images or embedded content that a site still needs. Report-only mode lets a team observe v...
Email security has two connected parts: protecting the mailbox people sign in to and making it harder for others to impersonate your domain. A secure ...
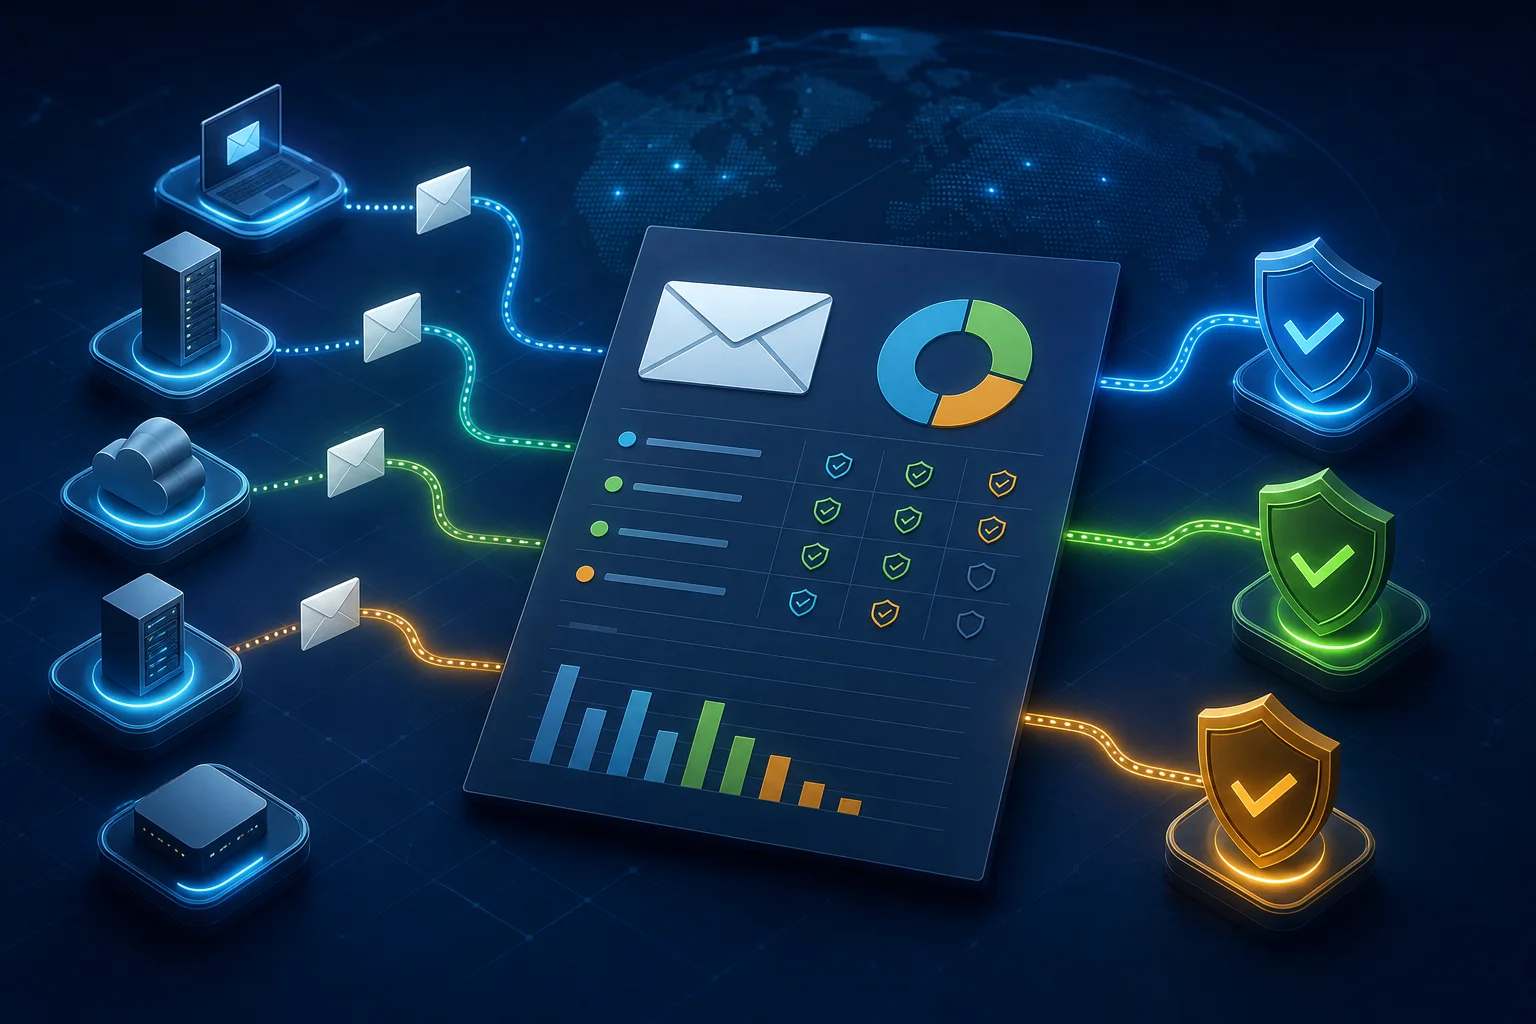
A DMARC aggregate report is a periodic view of mail sources claiming to send for a domain. It can help find legitimate systems that were missed during...
A secure Linux server is maintained through a sequence of ordinary decisions: install supported software, restrict who can administer it, expose only ...
Sponsors
Apps