PHP
Logging out should make the current browser stop presenting an authenticated session. Clearing a page variable is not enough: the server-side session ...
Email activation can confirm that a person can receive mail at an address, but it does not prove a legal identity. Treat the activation link as a temp...
A password reset link is a temporary credential. Anyone who obtains it may be able to change the account password, so the token must be difficult to g...
A “remember me” checkbox creates a credential that lasts longer than the current browser session. Treat it like a password reset token: someone who st...
A login can appear successful and still lose its session on the next request. PHP sessions depend on a cookie reaching the browser and the server bein...
JSON decoding can fail because a request is malformed, and encoding can fail because a value cannot be represented as valid JSON. If a program ignores...
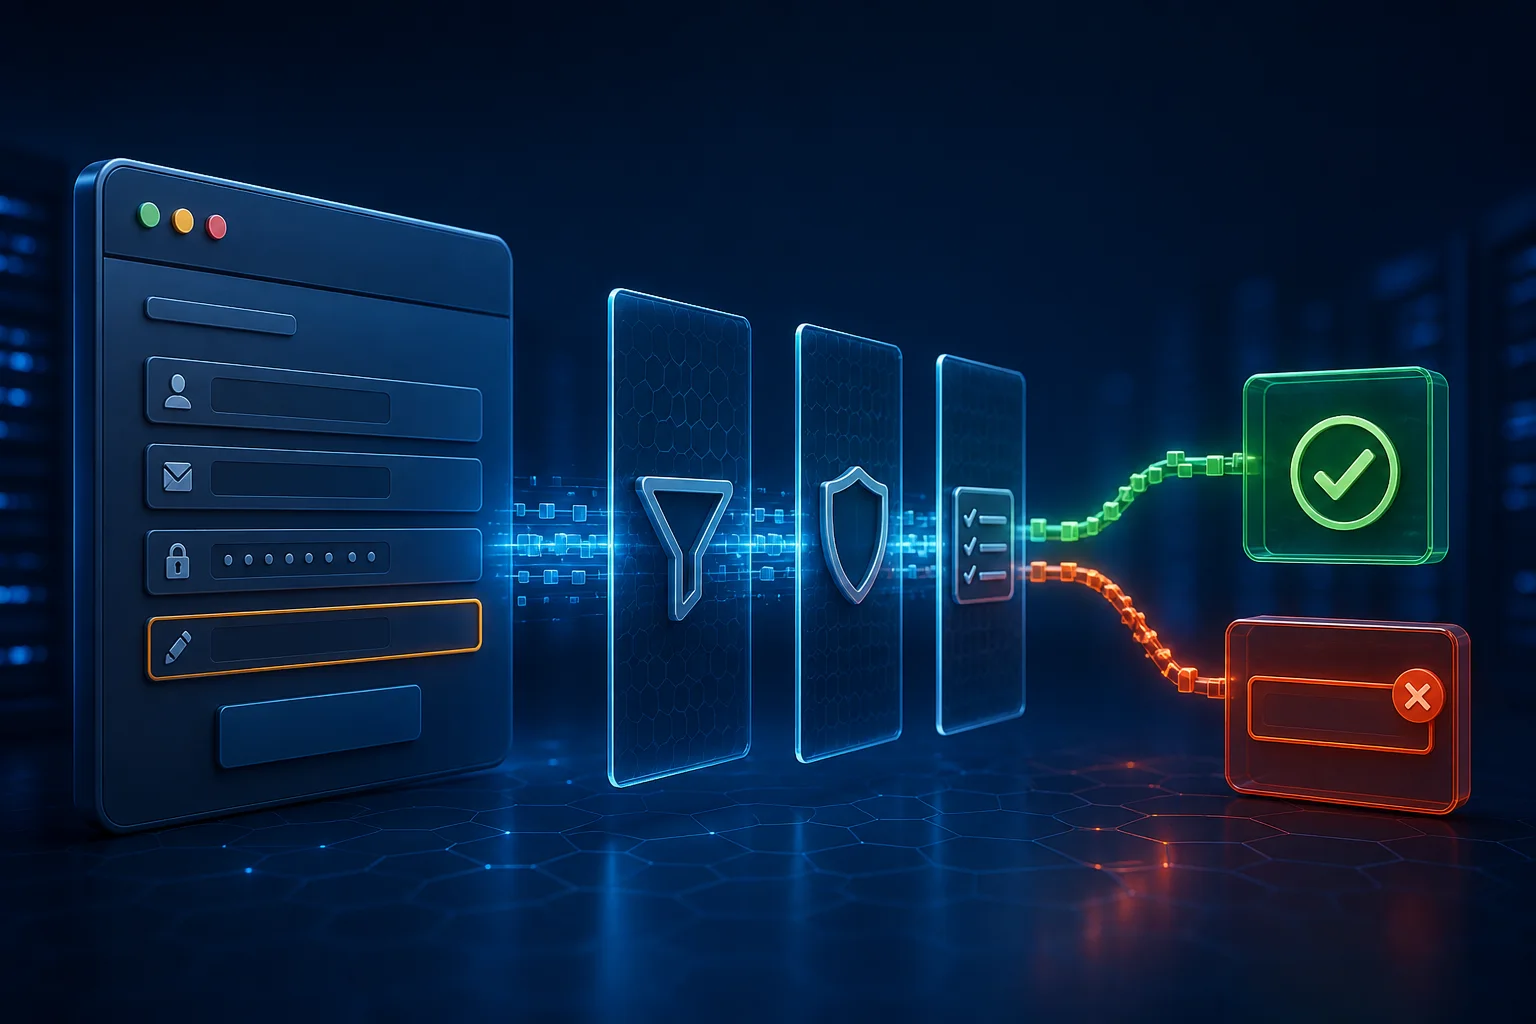
When filter_input() returns NULL, it is tempting to treat the value as an empty string or a failed validation. Those are different states. A missing i...
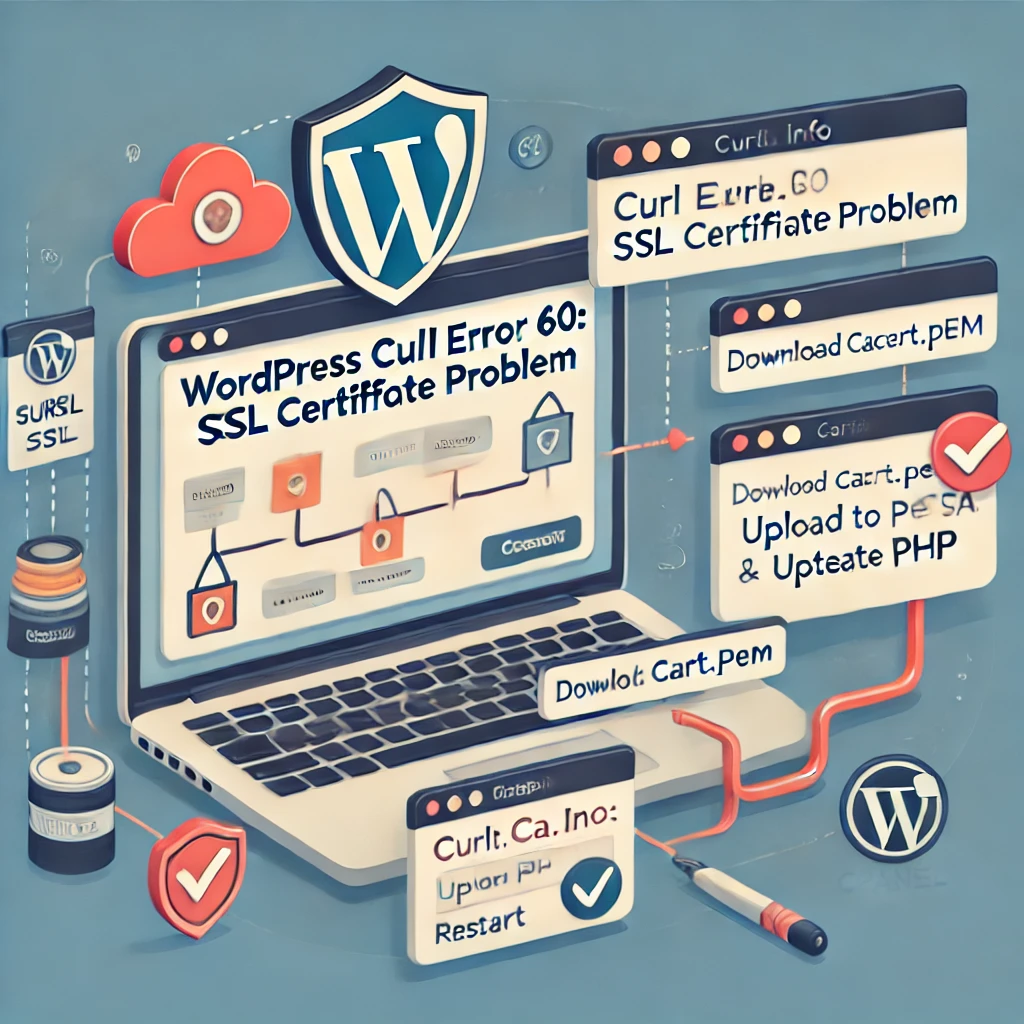
cURL error 60 means certificate verification failed during a connection. In WordPress it may appear while contacting an update service, payment provid...
PHP's built-in functions can reduce repetitive code, but misreading a return value introduces new bugs. Distinguish validation from sanitization, and ...
JSON Web Token (JWT) is a secure and widely used method for authentication and authorization in web applications. In this guide, we’ll build a basic a...
Sponsors
Apps